
A strong visitor management policy should make three things clear: who may enter the workplace, what information is collected, and who is responsible for each visit. It should protect employees, visitors, facilities, and sensitive information without turning reception into a confusing approval queue. The most effective policy combines advance registration, host accountability, consistent check-in rules, accessibility and safety considerations, and defined retention limits. Use the template below as a starting point, then adapt it to your sites, security requirements, privacy obligations, and workplace culture.
This policy establishes a consistent approach for welcoming, identifying, supporting, and offboarding visitors at company workplaces. It applies to anyone entering a controlled workplace who is not an employee or otherwise authorized worker, including guests, candidates, contractors, vendors, delivery personnel, interviewees, customers, partners, and event attendees.
The policy should be guided by a few operating principles:
Different visitor types create different operational and security needs. Defining categories helps employees apply the policy consistently instead of making ad hoc decisions at the front desk.
Access should be limited to the areas and time period necessary for the visit. A visitor badge or digital credential should not be treated as a general authorization to move throughout the workplace. Restricted rooms, work areas, laboratories, production spaces, and other sensitive environments should have separate access requirements.
Hosts should register planned visitors before arrival whenever practical. A visitor registration record can include the visitor’s name, organization, arrival date and time, host, purpose of visit, expected duration, accessibility or accommodation needs, and any site-specific approval requirement.
Arrival instructions should tell visitors where to go, whom to contact, what identification may be required, and whether they need to complete a confidentiality agreement, safety briefing, or other prerequisite. Instructions should also explain what happens if the host is unavailable.
For recurring contractors or vendors, workplace teams should avoid creating indefinite access by default. Each access arrangement should have an owner, a defined end date or review point, and a process for revocation when the engagement ends.
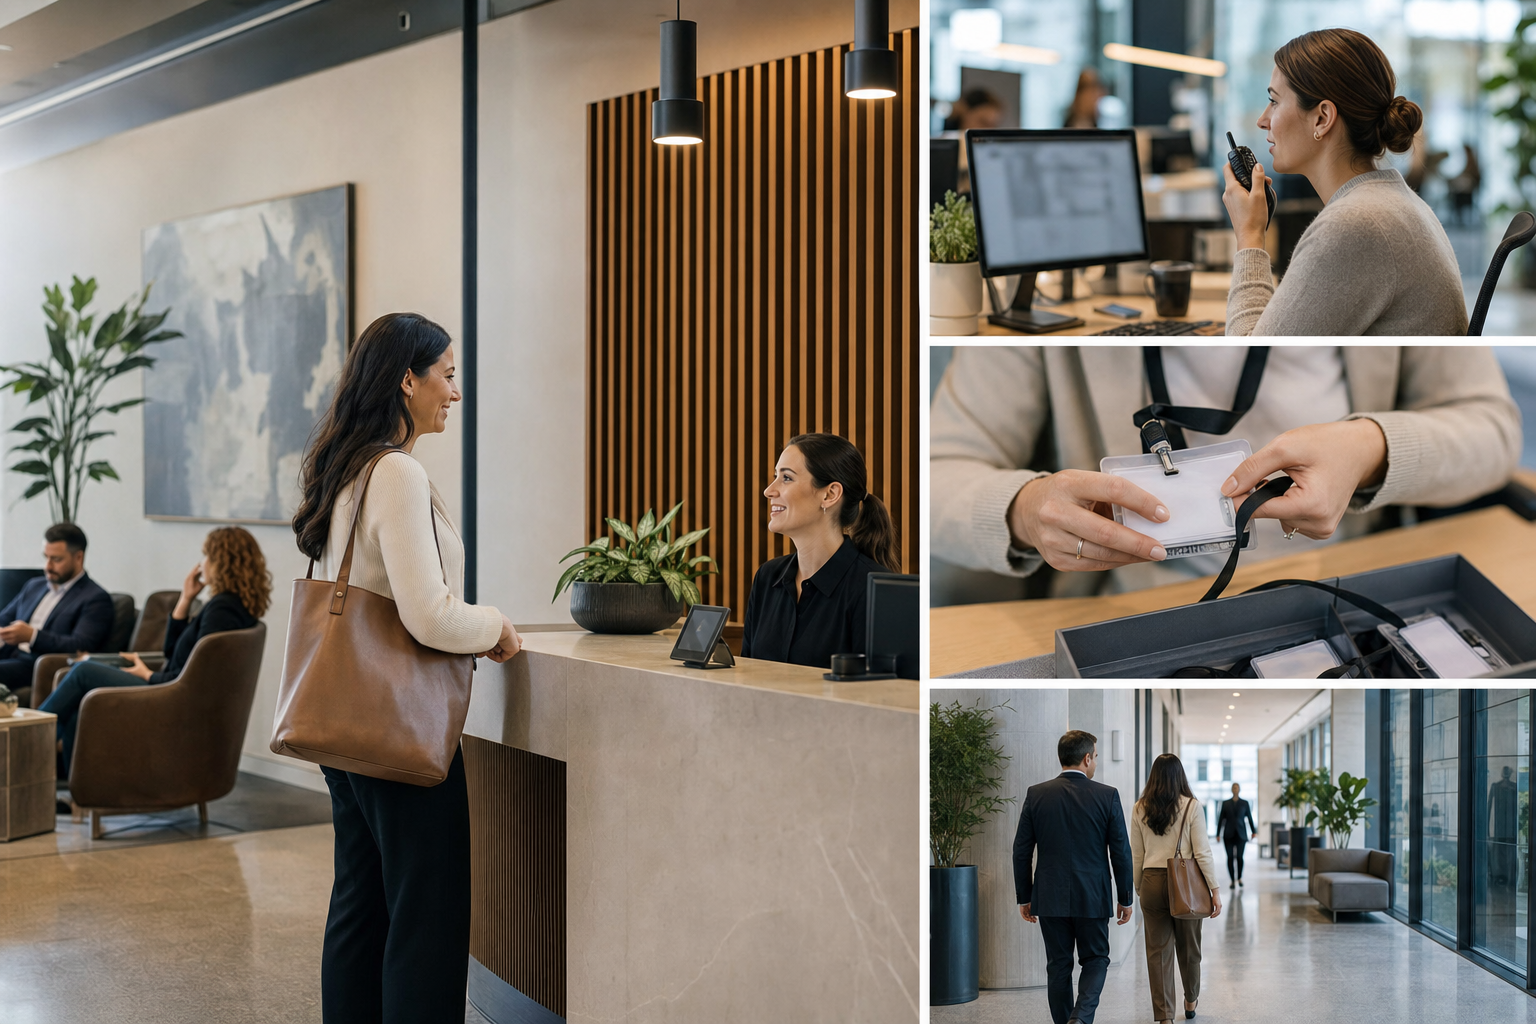
Every site should document its check-in method. Depending on the workplace, this may include a staffed reception desk, a self-service check-in station, a mobile registration experience, or a combination of approaches. The method matters less than the consistency of the controls around it.
At check-in, the visitor should be matched to a registration record or verified by the host or designated workplace team. The site should issue a visible visitor credential when appropriate and explain where the visitor may go, whether an escort is required, and how to request assistance.
Hosts should be notified when their visitor arrives. If a host does not respond within the site’s defined waiting period, the visitor should be directed to a clear escalation path rather than left without guidance. Reception and workplace teams should never be expected to improvise access decisions without an approved rule.
A connected visitor management system can help centralize invitations, arrival notifications, visitor records, badges, and host workflows. It should support the policy, not replace judgment about sensitive visitors, unusual circumstances, or restricted areas.
The host is responsible for preparing the visitor’s experience and following the site’s rules. Before the visit, the host should provide accurate arrival details, confirm that the meeting location is available, and identify any special access or accommodation needs.
During the visit, the host should meet the visitor promptly or arrange an approved delegate. The host should ensure that the visitor remains within authorized areas, follows safety and confidentiality requirements, and is accompanied when the site requires an escort.
At the end of the visit, the host or reception team should confirm departure and recover any temporary credential or equipment. Hosts should not lend employee badges, allow visitors to follow employees through secured doors, or bypass check-in for convenience.
Visitor procedures should be part of the workplace emergency plan, not a separate reception exercise. The company should maintain a current way to identify visitors onsite and include them in evacuation, shelter-in-place, severe weather, medical emergency, and other applicable procedures.
Each site should define who is responsible for visitor accountability during an emergency. That person or team should know how to access the visitor list, communicate with hosts, and coordinate with emergency responders while respecting privacy and security requirements.
Accessibility should be considered before arrival. Registration and check-in should offer a practical way for visitors to communicate mobility, hearing, visual, language, or other access needs. Routes, entrances, reception areas, meeting rooms, and emergency procedures should be evaluated for usability rather than assumed to be accessible.
Visitors should receive safety information appropriate to the site and their activities. Contractors working in higher-risk environments may need additional induction, personal protective equipment, supervision, or proof of authorization before entering operational areas.
The policy should state what visitor information is collected, why it is needed, who can access it, how long it is retained, and how it is deleted or securely disposed of. Requirements may vary by location and by the type of information collected, so legal, privacy, security, and facilities stakeholders should review the final policy.
Access to visitor records should be limited to people with a legitimate operational, security, safety, or compliance need. Reports and exports should be protected, and sensitive information should not be displayed where other visitors or passersby can view it.
Photographs, identification details, confidentiality acknowledgments, and other higher-sensitivity information should have a specific purpose and retention rationale. Do not collect information simply because a system makes it available. A privacy notice should explain the processing in clear language where required.
Exceptions should be uncommon, documented, and owned by a named role. The policy should identify who may approve after-hours visits, unregistered visitors, access to restricted areas, large events, media visits, or visits involving sensitive company information.
A visitor may be denied or delayed when identity cannot be verified, the host cannot be confirmed, required authorization is missing, the visitor presents a safety concern, or the visit conflicts with site restrictions. Employees should communicate the decision respectfully and provide an escalation route when appropriate.
Incidents such as badge misuse, tailgating, lost credentials, unauthorized access, threatening behavior, or an unaccounted visitor should be reported through the company’s established security or workplace channel. The response should focus on immediate safety, accurate documentation, and proportionate follow-up.
Assign ownership for the policy to a function that can coordinate workplace operations, security, facilities, people teams, privacy, and local site leaders. The owner should maintain the approved policy, site variations, escalation contacts, training materials, and review schedule.
Review visitor operations using practical signals rather than volume alone. Useful questions include whether hosts receive timely arrival notifications, whether visitors understand where to go, whether badges are returned, whether emergency lists are reliable, and whether employees can explain the process. Feedback from reception teams, hosts, visitors, and security partners can identify friction that a visitor count will not show.
Organizations that also coordinate workplace requests can use a shared operating model for ownership, routing, service expectations, and escalation. This helps visitor needs connect with facilities, IT, access, and meeting coordination without making the visitor responsible for internal handoffs.
Use this checklist before publishing or materially changing the policy:
Advance registration is preferable for planned visits because it improves arrival communication and accountability. The policy should still define how reception handles unscheduled visitors, deliveries, emergencies, and other legitimate exceptions.
Ownership depends on the organization, but the policy should have one accountable owner and a cross-functional review group. Workplace operations, security, facilities, privacy, people teams, and local site leaders may all contribute requirements.
Set a regular review cycle and revisit the policy sooner when the workplace changes, a site opens or closes, access technology changes, an incident occurs, or applicable requirements change.

A workplace experience platform that brings your hybrid team together.